Attackers now move in seconds. Wiz, now part of Google Cloud, connects everything you build and run into one picture of real risk. Dito helps you put it to work across your security program.
The gap attackers are exploiting
Three years ago, attackers who broke into an environment typically took about eight hours to hand that access off to a second threat group. According to Mandiant’s M-Trends 2026 report, that hand-off now takes 22 seconds.
Most security programs weren’t built for that pace. The typical setup splits the work across separate tools:
- Code scanning lives in one tool.
- Cloud posture lives in another.
- Runtime detection lives in a third.
- AI adoption often isn’t tracked at all.
Each tool generates its own alerts, and none of them sees how a weakness in one layer connects to a weakness in another. Teams spend their days reconciling dashboards. Meanwhile, the real exposure hides in the gaps between tools: a vulnerable workload with an over-privileged identity and a path to sensitive data.
Closing that gap takes shared context, not another point product.
Wiz is now part of Google Cloud
In March 2026, Google completed its acquisition of Wiz, the cloud and AI security platform trusted by half of the Fortune 100. Wiz joined Google Cloud and kept its brand. It also kept its commitment to protecting customers across every major cloud: AWS, Microsoft Azure, Google Cloud, and Oracle Cloud.
That combination matters to security leaders:
- Wiz brings graph-based context that connects code, cloud, and runtime.
- Google Cloud brings Google Security Operations, Google Threat Intelligence, and Mandiant frontline expertise.
Together, they let you see risk, fix it at the source, and respond to threats as part of one security strategy, even when your workloads span multiple clouds.
What Wiz makes possible
See the risks that actually matter. The Wiz Security Graph maps how infrastructure, identities, vulnerabilities, data, and AI assets relate to one another. It surfaces “toxic combinations” that isolated alerts miss. One example is an internet-exposed virtual machine with an unpatched critical CVE and an identity that can reach a sensitive AI model. Instead of thousands of disconnected findings, your team gets a prioritized view of real attack paths.
Prove what’s exploitable before attackers do. The Wiz Red Agent acts as an AI-powered attacker. It continuously tests your web applications and APIs for the logic flaws that traditional scanners miss. Each finding comes with proof that it can be exploited, so your team knows what to fix first.
Fix problems where they start. Wiz traces cloud risk back to the code that introduced it and the person who owns it. The Wiz Green Agent finds the root cause of your highest-risk issues and writes remediation plans specific to your environment. Your team can turn those plans into pull requests or hand them to AI coding agents, with developers reviewing every change.
Detect and contain threats with humans in control. Wiz Defend adds real-time visibility into running workloads. The Wiz Blue Agent investigates alerts the way an experienced incident responder would and shows every step of its reasoning. Wiz Workflows lets your team decide which actions run automatically and which need human approval.
The Wiz platform, module by module
Every Wiz module shares the same Security Graph and connects to your clouds agentlessly through provider APIs by default. The result is a single, consistent view of risk from the first line of code to production.
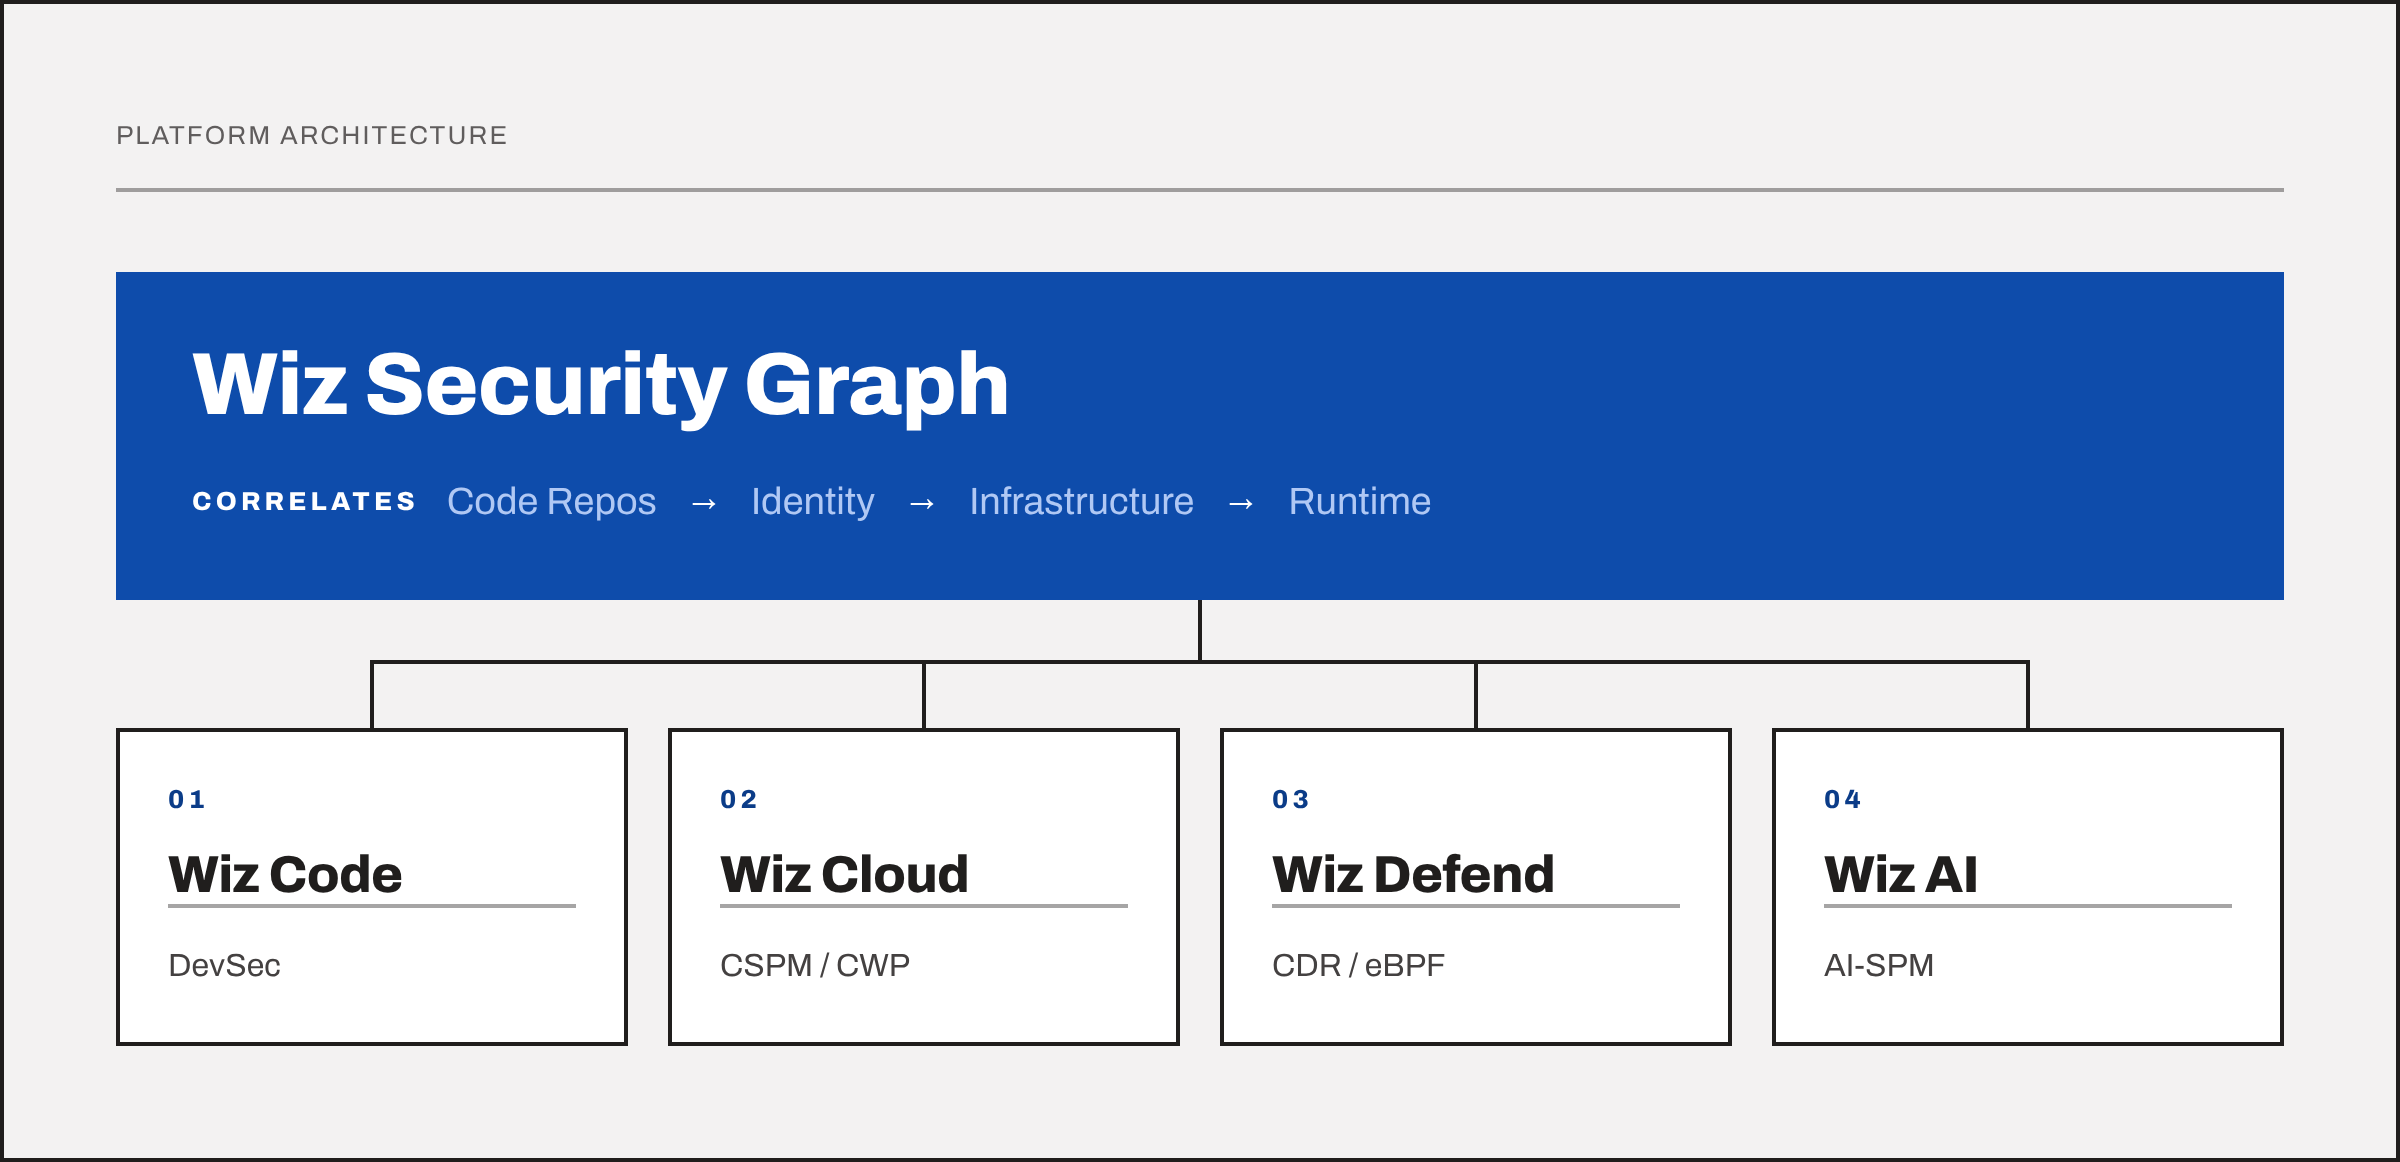
Wiz Code
Wiz Code brings security into the tools that developers and AI coding agents already use.
- Developer-native integrations: Plugins for VS Code, JetBrains, and Visual Studio, plus integrations with version control, CI/CD pipelines, the CLI, and Jira. It also connects to AI tools like Cursor through MCP.
- Pipeline scanning: Static application security testing (SAST), software composition analysis (SCA), Infrastructure as Code (IaC), and secrets scanning before code ships.
- Guardrails for AI-generated code: Built-in checks review prompts and scan AI-generated code inside IDEs and agent workflows before anything is committed.
- WizOS hardened images: Container base images with near-zero known vulnerabilities (CVEs), built from source, with a software bill of materials (SBOM) and signed provenance in every build.
- Wiz commits to patching critical CVEs within 7 days and high and medium CVEs within 14 days.
- Wiz research found a 94% median reduction in CVEs compared with equivalent open source images.
Wiz Cloud
Wiz Cloud shrinks the attack surface across AWS, Azure, Google Cloud, Oracle Cloud, and hybrid environments.
- Agentless posture management: Continuously assesses configurations and identity permissions through cloud APIs, and ranks exposure paths by real-world risk.
- Code-to-cloud tracing: Scans Terraform, CloudFormation, ARM templates, Dockerfiles, and Kubernetes manifests, then traces cloud misconfigurations back to the code that created them.
- Continuous compliance: Assesses environments against frameworks such as PCI DSS, SOC 2, HIPAA, and NIST, with reports ready for auditors.
Wiz Defend
Wiz Defend extends the platform into cloud detection and response (CDR).
- Lightweight runtime sensor: An eBPF-based sensor tracks process execution, container behavior, and network activity in real time. It also collects forensic evidence at the moment of detection.
- Correlated telemetry: Combines runtime signals with cloud audit logs (AWS CloudTrail, Azure Activity Logs, Google Cloud Audit Logs), identity provider records, and Kubernetes events.
- Investigation and response: Builds forensic timelines from initial access to command execution and maps activity to MITRE ATT&CK. Through Wiz Workflows, it can also trigger containment playbooks.
Wiz AI Application Protection Platform (AI-APP)
Wiz introduced AI-APP at RSAC 2026 as the next step beyond cloud-native application protection (CNAPP). It adds visibility, risk analysis, and runtime protection for AI applications to the same graph-powered platform.
- AI discovery and AI-BOM: Inventories models, agents, tools, training data, and AI frameworks, including IDE extensions. Teams can track approved AI tools and uncover shadow AI.
- Coverage wherever teams build: Supports managed AI services such as Vertex AI, Amazon Bedrock, and Azure AI. It also covers Databricks and agent platforms including Gemini Enterprise Agent Platform, Amazon Bedrock AgentCore, Microsoft Copilot Studio, and Salesforce Agentforce.
- Cross-layer risk analysis: Connects AI risk to the infrastructure, identities, and data around it, and maps findings to frameworks such as the OWASP Top 10 for LLM Applications.
- Runtime AI protection: Monitors models, workloads, and identities for prompt injection, data leakage, and unauthorized agent behavior.
Wiz Agents and Workflows
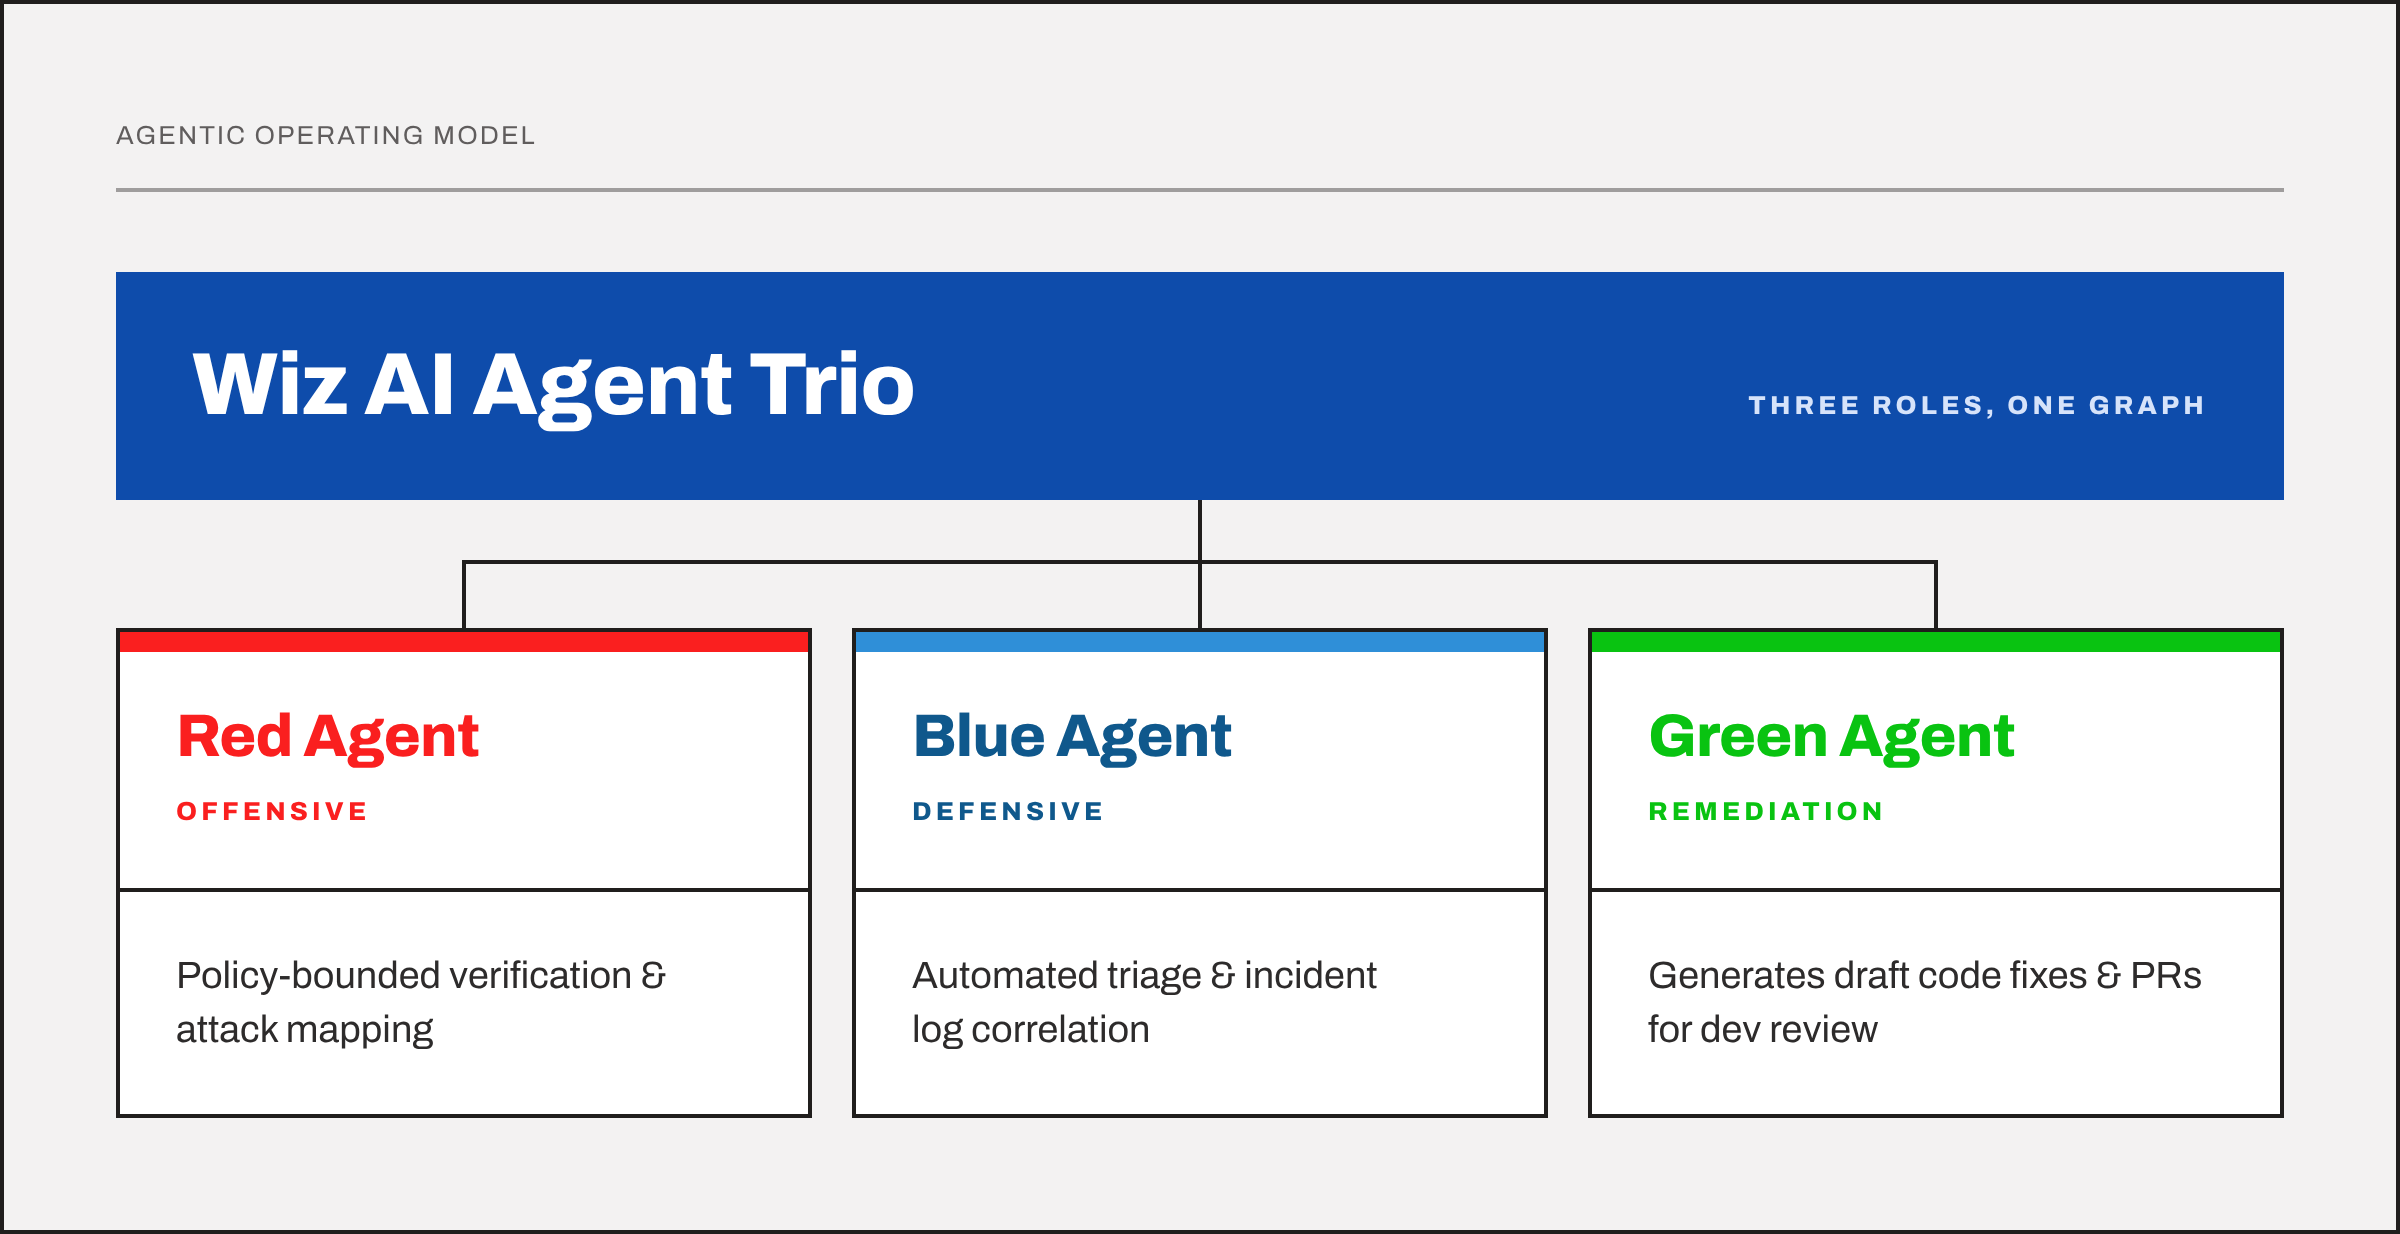
Three specialized AI agents automate validation, investigation, and remediation. Your team decides how much autonomy each one gets.
- Red Agent (generally available): An AI-powered attacker.
- Continuously finds and tests both known and unknown web applications and APIs, using Wiz’s live inventory of your environment.
- Confirmed high and critical findings become Wiz Issues, with Security Graph context attached.
- Blue Agent (generally available for Wiz Defend customers): An automated incident investigator.
- Gathers evidence from cloud telemetry, runtime signals, identity context, and related code changes.
- Delivers a clear verdict, with its full reasoning visible.
- Green Agent: A remediation engine.
- Investigates your highest-risk issues, identifies the root cause and the right owner, and writes step-by-step fixes such as CLI commands, Terraform updates, or Kubernetes changes.
- Fixes can become one-click pull requests, handoffs to coding agents, or actions triggered through the API or MCP.
- Wiz Workflows: A drag-and-drop canvas for orchestrating response.
- Each workflow can be human-led, keep a human in the loop, or run automatically, depending on each agent’s verdict and confidence level.
Where Wiz meets Google Security Operations
Wiz shows what’s exposed and what’s under attack across your clouds. Google Security Operations gives your security operations center (SOC) the place to act on it, alongside every other signal in your enterprise.
At Google Cloud Next ’26, Google updated how Wiz Defend detections flow into Google Security Operations and Mandiant Threat Defense, which makes automatic threat forwarding simpler to set up.
For your SOC, this means:
- Cloud and runtime detections arrive with Wiz’s code-to-cloud context already attached.
- Analysts can work those detections with Google Security Operations’ AI-driven triage and investigation.
- Every investigation is backed by Google Threat Intelligence and Mandiant expertise.
The connections extend across Google Cloud:
- Agent development: Teams building on Gemini Enterprise Agent Platform and Vertex AI get the same AI visibility they have everywhere else.
- API discovery: Wiz integrates with Google Cloud Apigee to find and assess APIs.
- Remediation: The Green Agent uses capabilities from CodeMender, Google DeepMind’s AI code-security agent, to trace risks back to source code.
How Dito helps
Dito is an approved Wiz Partner Alliance partner and a premier Co-Sell and Services Partner for Google Cloud. That puts us right where these two platforms meet. The Dito security team helps you:
- Deploy with intent. We connect Wiz across your cloud accounts and prioritize the toxic combinations that matter most to your business. We also configure guardrails that fit how your teams already build.
- Connect Wiz to your SOC. We route Wiz detections into Google Security Operations (or other SIEM) so your analysts investigate cloud threats with full context in the platform they already use.
- Put AI agents to work responsibly. We design Wiz Workflows that spell out where agents act on their own and where people stay in the loop.
- Drive real adoption. Security tools only work when developers use them. Our change management approach helps engineering teams make Wiz Code, WizOS images, and AI-assisted remediation part of their daily work.
Wiz protects AWS, Azure, and Oracle Cloud as well as Google Cloud. With Dito, you can secure your entire estate with the best of Google Cloud security solutions and certified experts to enable and support you.
See the platform through the lens of your environment
Book a Personalized Deep Dive of the Platform with the Dito security team. In this session, we’ll:
- Walk through the Wiz modules most relevant to your cloud mix and AI roadmap.
- Show how Wiz streamlines the security stack, or connects to existing security tools.
- Help you map where unified code, cloud, and AI security fits in your security strategy.
Recent Posts
On-Demand