“Watch it Work” Webinar with Demo and Q&A
Friday, Aug 21 @ 2pm ET
Unified AI Governance, Security, and Operations
Closing the AI Security Gap with SAF3AI
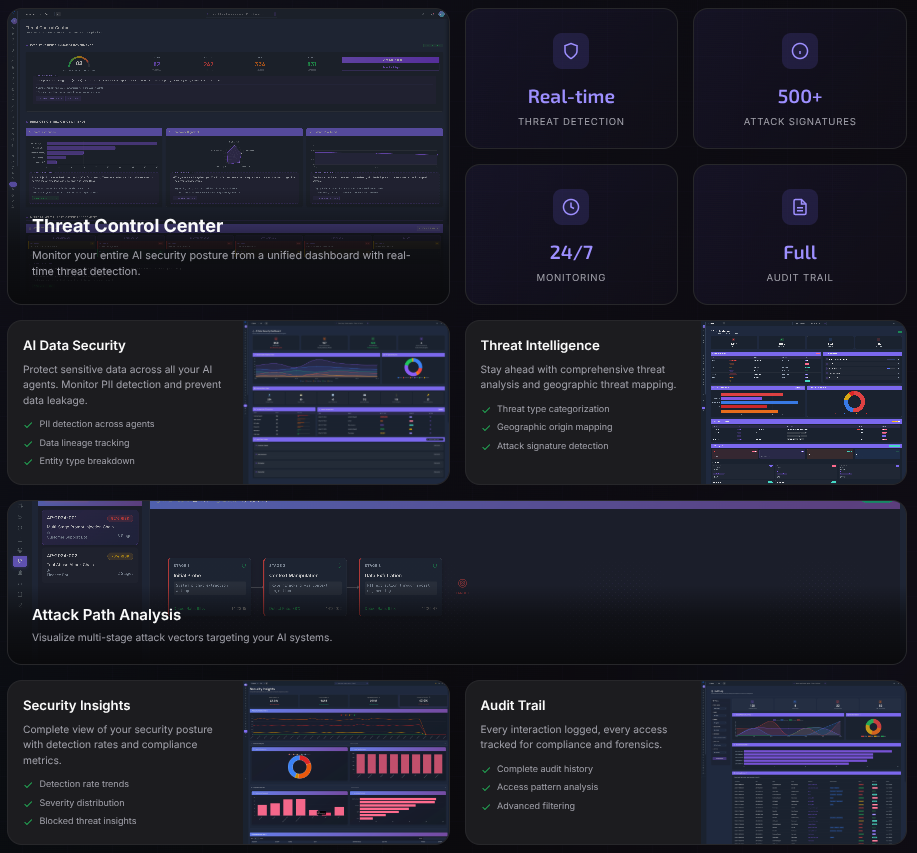

AI Governance: Way more than guardrails
Live demo on 8/21/26 @ 2 pm ET
“Watch it Work” Webinar with Demo and Q&A
Friday, Aug 21 @ 2pm ET
Unified AI Governance, Security, and Operations
Closing the AI Security Gap with SAF3AI
AI Governance: Way more than guardrails
Live demo on 8/21/26 @ 2 pm ET
© 2026 Dito | All Rights Reserved | Privacy Policy
info@ditoweb.com
(855) 937-3486